Our thinking

Cybersecurity: Legal implications and risk management

What's inside

In an increasingly interconnected world, cyber risk is firmly at the top of the boardroom agenda, and having an effective data breach response programme is no longer optional.

Cybersecurity crisis management

The internet knows no borders, neither do we. Our global team of cybersecurity response experts work across borders, combining data protection, privacy, regulatory, white collar and litigation expertise in order to deliver seamless crisis management and legal advice, whenever and wherever needed.

The digitalization and free flow of information has transformed global business. However, with increased opportunities have come new and increased risks, together with complex legislative regimes that can vary significantly by jurisdiction, and are constantly evolving. Even the most conscientious company can become the victim of a cybersecurity incident, such as the stealing of client or company information, or a ransomware attack. We work with a wide range of multinational companies to manage their cybersecurity risks, developing rapid response plans, providing time-critical crisis management advice, and working with clients to manage any resulting legal issues that may arise. 


Key issues

Why?

  • Reputation
  • Fines
  • Breach of contract
  • M&A due diligence
  • Insurance
  • Proprietary information
  • Litigation
  • Criminal offences
  • Negligence

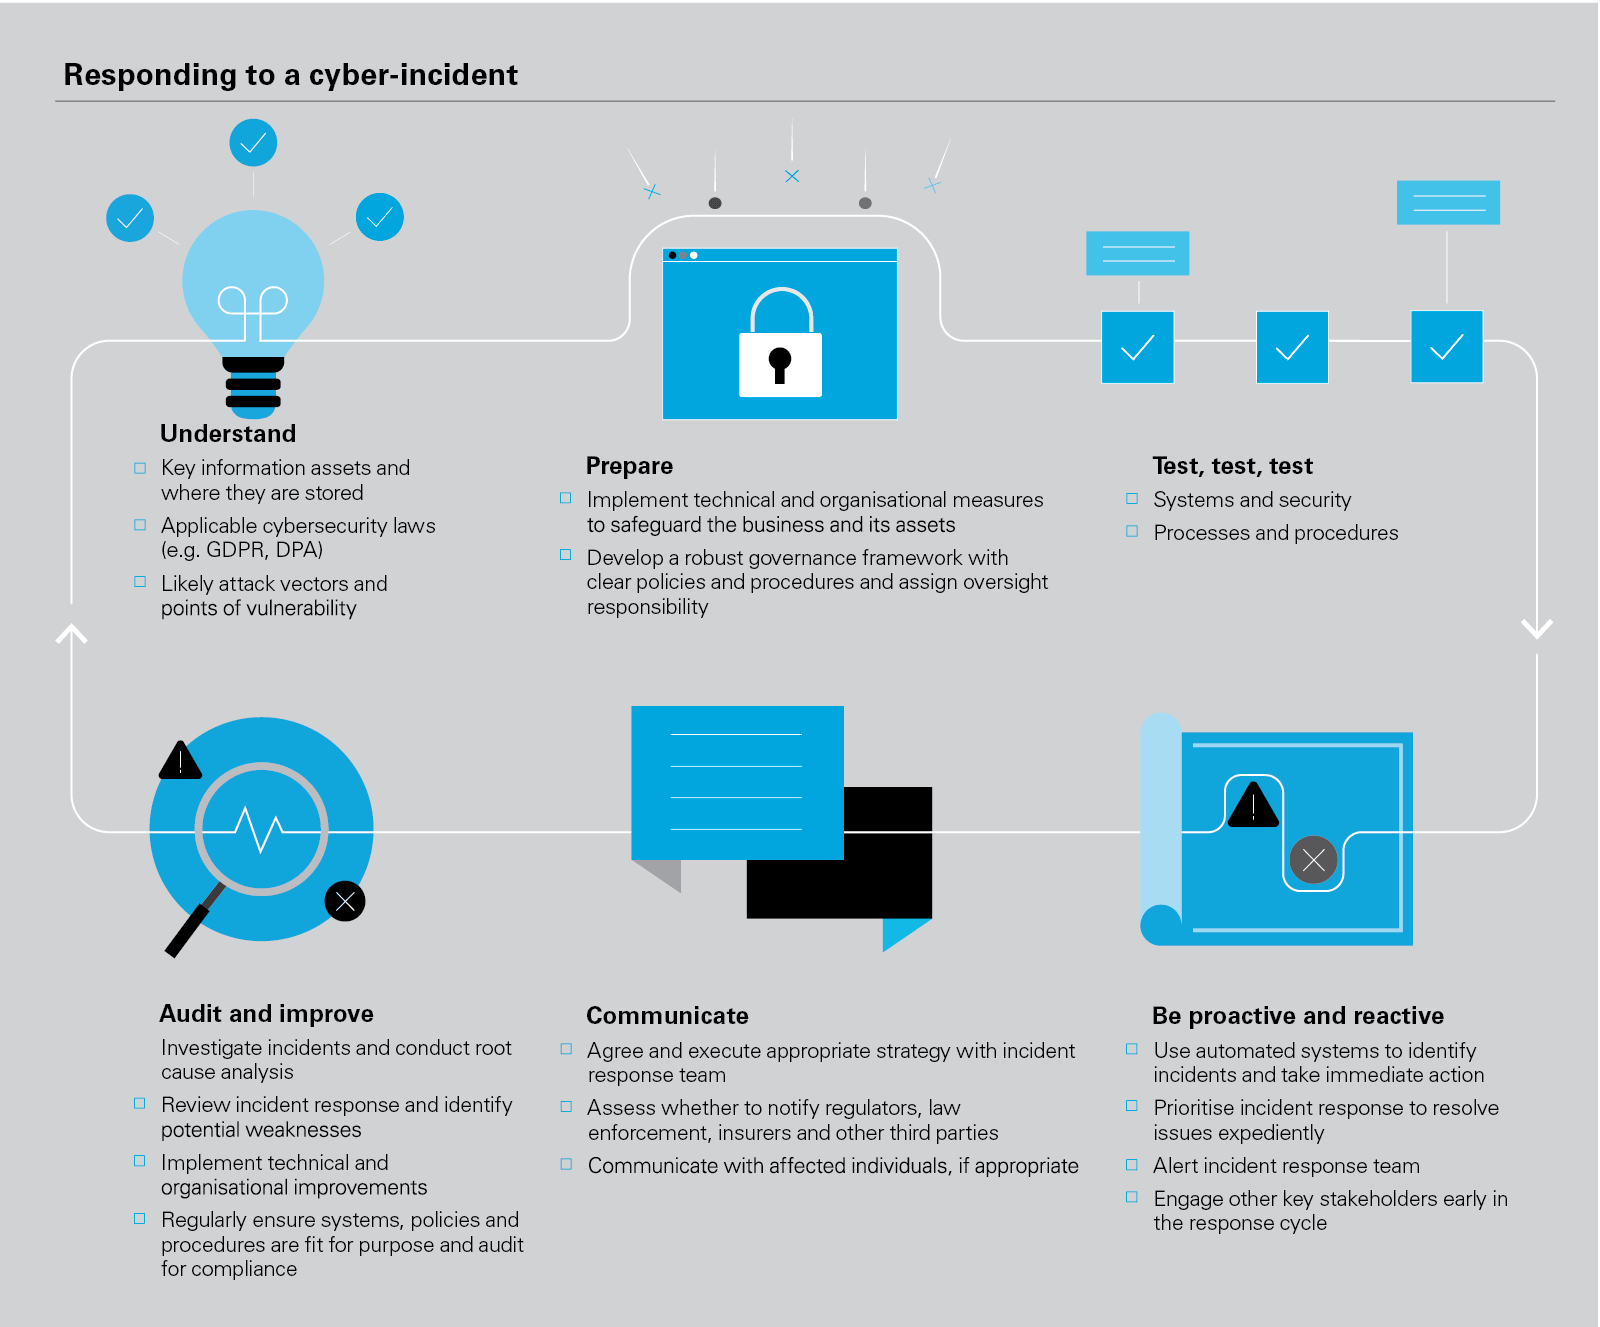
Be prepared

Risk Assessment

  • Key Information
  • Assets
  • Key Systems
  • Threat Analysis
  • Security Measures

Toolkit

  • Scripts
  • Internal and 
    External
  • Communications
  • Employee contacts
  • Response Plan
  • Live Training
  • Business Continuity Plan

Key considerations

Customer/individual rights

  • Requests for data
  • Data Protection Authority Complaints
  • Group litigation orders
  • Resolution mechanisms

B2B relationships

  • Contractual obligations
  • Contractual liability
  • Tort

Reputation management

  • Media strategy
  • Customer interaction
  • Employee engagement

Commercial

  • Proprietary
  • Information/Trade Secrets
  • System Disruption

Regulatory issues

  • Data Protection Authority
  • Financial Regulators
  • Market authorities
  • Other regulators

Privacy & data protection

  • Jurisdictions involved
  • Reporting obligations
    • individuals
    • authorities

Evidence

  • Law Enforcement Involvement
  • Legal Privilege
  • Preservation of Evidence

Response

Crisis Team

  • Legal (internal and external)
  • IT/IT Forensics
  • PR
  • Regulatory
  • DPO
  • Executive committee
  • HR
  • Vendor manager

Key Actions

  • Work with forensic investigators to:
    • Identify and contain breach
    • Gather/preserve evidence
    • Maximise legal privilege coverage
  • Contact crisis team
  • Bring in external partners
  • Identify key risks and priorities based on nature of breach
  • Assess notification requirements
  • Communications
  • Regulatory notifications


Articles

2025

Reform to the UK’s cybersecurity regime incoming

Changes are coming to the UK’s cybersecurity legal landscape. The new Cyber Security and Resilience (Network and Information Systems) Bill aims to expand legal requirements to more sectors, tighten incident reporting rules, give the Government stronger powers to tackle cyber threats, and ramp up fines for serious breaches. 

Read 6 min. article

NIS 2: One year later

Member States were required to implement the NIS 2 Directive ("NIS 2") into national law by 17 October 2024. One year on, many EU Member States have failed to meet the transposition deadline, creating confusion and increasing compliance complexity for organisations across the EU.

Read 3 min. article

Cyber Resilience Act: The clock is ticking for compliance

The Cyber Resilience Act (the "CRA") entered into force on 10 December 2024 and applies in full from 11 December 2027. Manufacturers of in-scope products should start the compliance journey as soon as possible to avoid impacts to the product development cycle and non-compliance risk exposure.

Read 5 min. article

Navigating NIS 2: Mastering Compliance and Risk in a Fragmented Cybersecurity Landscape

White & Case Partners John Timmons and Clara Hainsdorf explore the key issues for organizations grappling with NIS 2 compliance in light of the complex implementation landscape. 

Read 1 min. article

Ransomware Payments: New legislative proposals in the UK

On 14 January 2025, the Home Office opened a public consultation (the "Consultation") on proposals seeking to address the growing threat and impact of ransomware in the UK.

Read 6 min. article
data centres

2024

NYDFS Releases Artificial Intelligence Cybersecurity Guidance For Covered Entities

On October 16, 2024, the New York State Department of Financial Services (the "DFS"), under its Cybersecurity Regulation—23 NYCRR Part 500—issued a memorandum providing guidance on the risks posed by artificial intelligence ("Guidance Memo").

Read 8 min. article

SEC Will Prioritize AI, Cybersecurity, and Crypto in its 2025 Examination Priorities

On October 21, 2024, the US Securities and Exchange Commission ("SEC") Division of Examinations ("Examination Division") announced its 2025 Examination Priorities ("Report"). Investment advisers and broker-dealers should ensure that policies, procedures and surveillance efforts related to these priorities address concerns outlined in the Report.

Read 3 min. article

SEC Enforcement Heats up on Key Public Company Topics: Cyber Disclosure, Director Independence and Regulation FD

The U.S. Securities and Exchange Commission's ("SEC") Division of Enforcement has recently brought a spate of enforcement actions relating to key topics for public companies. These include enforcement actions related to cybersecurity incident disclosure, director independence and Regulation Fair Disclosure ("Reg FD") violations, which are described below, and actions based on Section 13 and 16 beneficial ownership filings, as discussed in our prior alert.

Read 13 min. article

Judge Rejects SEC’s Aggressive Approach to Cybersecurity Enforcement

On July 18, 2024, a New York federal judge dismissed most of the US Securities and Exchange Commission's ("SEC") claims against SolarWinds Corp. ("SolarWinds" or the "Company") and its Chief Information Security Officer ("CISO"), Timothy G. Brown, in connection with the Company's cybersecurity practice.

Read 10 min. article

NIS 2 Directive: Navigating the challenges of implementation, impact, and scope

The NIS 2 directive establishes a regulatory framework aimed at improving the level of cybersecurity across the EU.

Read 1 min. article

SEC’s Corp Fin Director Issues Statement on Cybersecurity Incident Disclosures

On May 21, 2024, the SEC's Director of the Division of Corporation Finance issued a statement on cybersecurity incident disclosures in light of the SEC's new cybersecurity disclosure rules. Our summary of this statement and key take-aways from White & Case's survey of cybersecurity disclosures is below.

Read 6 min. article

2023

The SEC’s Charges Against SolarWinds and its Chief Information Security Officer Provide Important Cybersecurity Lessons for Public Companies

On October 30, 2023, the US Securities and Exchange Commission ("SEC") announced that it filed charges against SolarWinds Corp. ("SolarWinds" or the "Company") and its Chief Information Security Officer ("CISO") in connection with the SEC Division of Enforcement's ("Enforcement Division") investigation of a cyberattack.

Read 10 min. article

SEC Adopts Mandatory Cybersecurity Disclosure Rules

On July 26, 2023, the Securities and Exchange Commission ("SEC"), in a 3-2 vote, adopted rules that will require public companies to make prescribed cybersecurity disclosures.

Read 22 min. article

Shaping the future of digital and cybersecurity governance

In this brief three-minute video, London-based partner Lawson Caisley, Chair of White & Case's Global Cyber Risk Committee, shares his insights on governing cyber risk at the corporate level and some of the challenges of cyber risk management in the boardroom. Filmed at the Digital Directors Network (DDN) Domino 2023 conference on digital and cybersecurity governance.

Read 1 min. article
cybersecurity_square_800x800_4

Prioritizing cybersecurity at the corporate level

In this short three-minute video, Washington, DC–based partner F. Paul Pittman discusses the implications of the proposed new SEC rules on cybersecurity governance and what corporate boards can do now. Filmed at the Digital Directors Network (DDN) Domino 2023 conference on digital and cybersecurity governance.

Read 1 min. article
digital mesh

Cybersecurity Developments and Legal Issues

The potential for cybersecurity threats and attacks looms large and the technology companies developing new products and services play a constant game of cat-and-mouse with hackers and cybercriminals for control of cyberspace. Here are six points to consider when analyzing cybersecurity risks and protections.

Read 9 min. article
client alert image

Directors face personal liability over cybersecurity failures

In an article for The Times, White & Case partner Lawson Caisley discusses why it could become increasingly common for UK directors to "face personal liability and regulatory censure as a result of their company suffering or mishandling a cyberbreach".

Read 1 min. article
wafer circuit detail

2022

Director liability for cyber breaches: transatlantic warning signs?

Two legal cases in the US in the past month suggest that regulators and prosecutors are becoming more determined to take personal action against directors and senior executives who fail to deal adequately with cyber security breaches.  

Read 3 min. article
arrow

SEC Proposes Mandatory Cybersecurity Disclosure Rules

On March 9, 2022, the Securities and Exchange Commission ("SEC") proposed rules that would require public companies to make prescribed cybersecurity disclosures.

Read 14 min. article

2021

Legal 500's In-House Lawyer Magazine Autumn - Commercial Litigation Focus (Germany)

In The Legal 500's newly released In-House Lawyer Magazine a group of White & Case lawyers has contributed a legal briefing on trends in German commercial litigation.

Read 1 min. article
magazine pile

AAA plc & ors v Persons Unknown: Cyber Activism or Blackmail?

In recent years, demands for payments in cryptocurrencies have become the ransom of choice for cyber extortionists and other online frauds. As a result, the English Court's powers are increasingly being called upon.

Read 5 min. article
orange background

Contacts

Director liability for cyber breaches: transatlantic warning signs?

Alert
|
3 min read

Two legal cases in the US in the past month suggest that regulators and prosecutors are becoming more determined to take personal action against directors and senior executives who fail to deal adequately with cyber security breaches.  

At the beginning of October, Uber's former chief security officer was found guilty of criminal obstruction charges for failing to report a cyber breach to the authorities. This is believed to be the first time a US company executive has been criminally prosecuted over a cyber breach, and he now faces a prison sentence of up to eight years. Earlier this week, the Federal Trade Commission (FTC) announced that it had taken action against the CEO of Drizly (an online drinks delivery business) over the company’s security failures which led to a cyber breach that exposed the personal information of 2.5 million customers.

Given the global nature of regulatory trends and the fact that cyber breaches are increasingly a fact of business life, UK-based directors will be justifiably concerned at the prospect of a potential increase in the risk of personal liability arising from cyber breaches. However, a closer look at the facts of each of these cases suggests that aggravating factors prompted the authorities to target the individuals concerned.

In the first case, the criminal charges against Uber's former chief security office (James Sullivan) arose from the fact that, when the relevant cyber breach occurred in 2016, Uber was already under investigation by the FTC for an earlier cyber breach in 2014. The 2016 breach involved a hacker accessing customer records and demanding a US$100,000 payment, which was ultimately paid by Mr Sullivan's team. Mr Sullivan did not inform the FTC of the incident despite its ongoing investigation, and prosecutors alleged that he also took steps to conceal the incident within the company. Mr Sullivan's actions led to him being fired by Uber. 

In the second case, the FTC's decision to take action against the CEO as well as the company itself was driven by the fact that both were alerted to problems with the company's security procedures following a cyber attack two years earlier. Despite this, the company failed to implement basic cyber security measures while publicly claiming to have appropriate protections in place. The FTC's proposed order requires the company and the CEO to implement an information security programme to protect customer data. The FTC stated that this "ensures the CEO faces consequences for the company's carelessness".

Both these cases therefore involved aggravating factors that may place them outside of a 'typical' scenario where directors are faced with a cyber breach and try their best to deal with it honestly and reasonably. 

Turning to the UK, while it is the case that directors could face personal liability and regulatory censure as a result of their company suffering or mishandling a cyber breach, we have seen very few attempts to hold directors or senior managers personally liable in such circumstances. To date, legal claims and regulatory action have been mainly directed at the company suffering the breach. However, directors should not be complacent. UK regulators have long made clear their view that cyber security is a board level issue that requires serious and meaningful senior engagement. Directors must therefore assume that, like the FTC, UK regulators will be looking very closely at the conduct of individual directors in relation to any cyber breach suffered by their company and that, if similar aggravating factors were present, action against individual directors might be considered.

In addition, attempts to hold directors personally liable for negligence and breach of duty are becoming more common in the English courts, for example in relation to ESG-related issues. The fact that cyber security is now firmly established as a key business risk means that directors can increasingly expect a cyber breach suffered by their company to result in more pressure to demonstrate that they had taken reasonable steps both to prevent a breach and to prepare to handle any breach that occurred. 

Against that backdrop, UK boards would be well advised to heed the FTC's warning: "CEOs who take shortcuts on security should take note". 


White & Case means the international legal practice comprising White & Case LLP, a New York State registered limited liability partnership, White & Case LLP, a limited liability partnership incorporated under English law and all other affiliated partnerships, companies and entities.  

This article is prepared for the general information of interested persons. It is not, and does not attempt to be, comprehensive in nature. Due to the general nature of its content, it should not be regarded as legal advice.

Top