Our thinking

Cybersecurity: Legal implications and risk management

What's inside

In an increasingly interconnected world, cyber risk is firmly at the top of the boardroom agenda, and having an effective data breach response programme is no longer optional.

Cybersecurity crisis management

The internet knows no borders, neither do we. Our global team of cybersecurity response experts work across borders, combining data protection, privacy, regulatory, white collar and litigation expertise in order to deliver seamless crisis management and legal advice, whenever and wherever needed.

The digitalization and free flow of information has transformed global business. However, with increased opportunities have come new and increased risks, together with complex legislative regimes that can vary significantly by jurisdiction, and are constantly evolving. Even the most conscientious company can become the victim of a cybersecurity incident, such as the stealing of client or company information, or a ransomware attack. We work with a wide range of multinational companies to manage their cybersecurity risks, developing rapid response plans, providing time-critical crisis management advice, and working with clients to manage any resulting legal issues that may arise. 


Key issues

Why?

  • Reputation
  • Fines
  • Breach of contract
  • M&A due diligence
  • Insurance
  • Proprietary information
  • Litigation
  • Criminal offences
  • Negligence

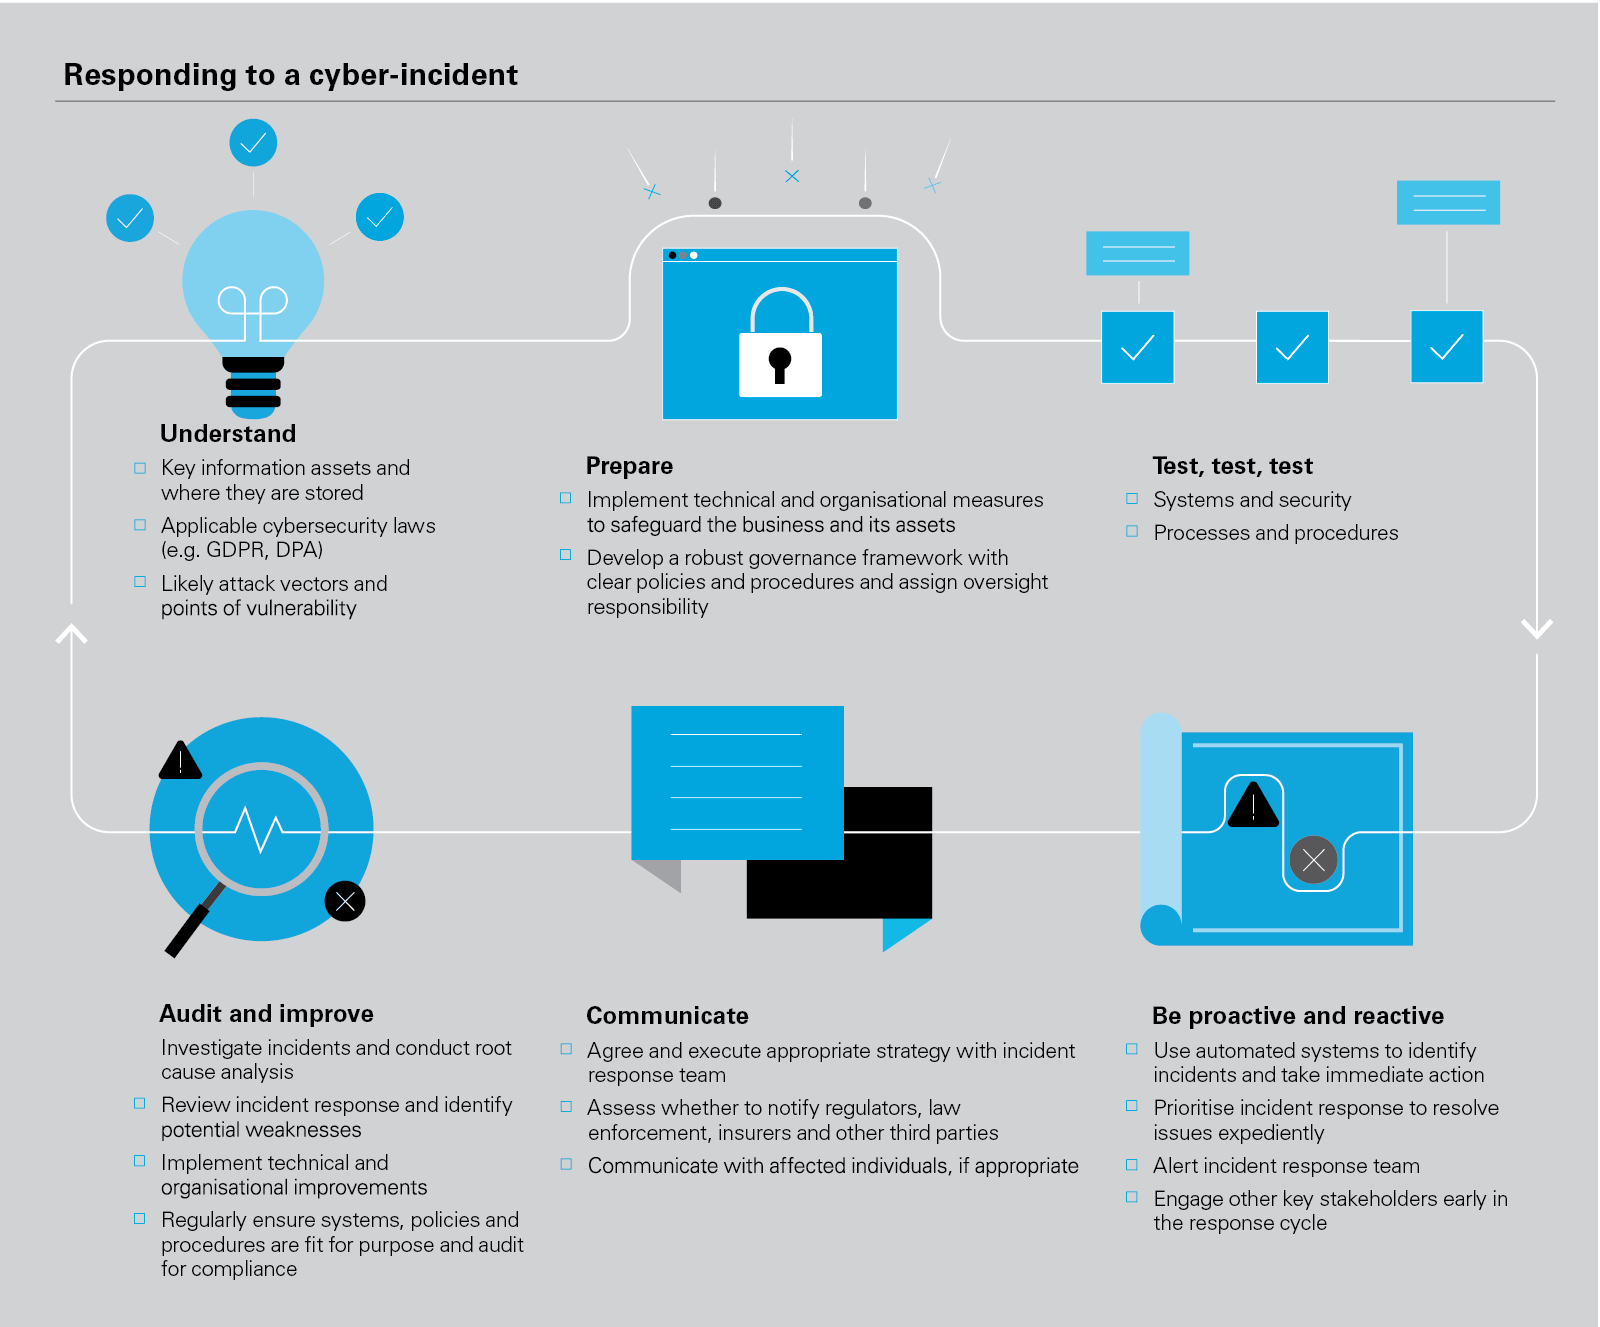
Be prepared

Risk Assessment

  • Key Information
  • Assets
  • Key Systems
  • Threat Analysis
  • Security Measures

Toolkit

  • Scripts
  • Internal and 
    External
  • Communications
  • Employee contacts
  • Response Plan
  • Live Training
  • Business Continuity Plan

Key considerations

Customer/individual rights

  • Requests for data
  • Data Protection Authority Complaints
  • Group litigation orders
  • Resolution mechanisms

B2B relationships

  • Contractual obligations
  • Contractual liability
  • Tort

Reputation management

  • Media strategy
  • Customer interaction
  • Employee engagement

Commercial

  • Proprietary
  • Information/Trade Secrets
  • System Disruption

Regulatory issues

  • Data Protection Authority
  • Financial Regulators
  • Market authorities
  • Other regulators

Privacy & data protection

  • Jurisdictions involved
  • Reporting obligations
    • individuals
    • authorities

Evidence

  • Law Enforcement Involvement
  • Legal Privilege
  • Preservation of Evidence

Response

Crisis Team

  • Legal (internal and external)
  • IT/IT Forensics
  • PR
  • Regulatory
  • DPO
  • Executive committee
  • HR
  • Vendor manager

Key Actions

  • Work with forensic investigators to:
    • Identify and contain breach
    • Gather/preserve evidence
    • Maximise legal privilege coverage
  • Contact crisis team
  • Bring in external partners
  • Identify key risks and priorities based on nature of breach
  • Assess notification requirements
  • Communications
  • Regulatory notifications


Articles

2025

Reform to the UK’s cybersecurity regime incoming

Changes are coming to the UK’s cybersecurity legal landscape. The new Cyber Security and Resilience (Network and Information Systems) Bill aims to expand legal requirements to more sectors, tighten incident reporting rules, give the Government stronger powers to tackle cyber threats, and ramp up fines for serious breaches. 

Read 6 min. article

NIS 2: One year later

Member States were required to implement the NIS 2 Directive ("NIS 2") into national law by 17 October 2024. One year on, many EU Member States have failed to meet the transposition deadline, creating confusion and increasing compliance complexity for organisations across the EU.

Read 3 min. article

Cyber Resilience Act: The clock is ticking for compliance

The Cyber Resilience Act (the "CRA") entered into force on 10 December 2024 and applies in full from 11 December 2027. Manufacturers of in-scope products should start the compliance journey as soon as possible to avoid impacts to the product development cycle and non-compliance risk exposure.

Read 5 min. article

Navigating NIS 2: Mastering Compliance and Risk in a Fragmented Cybersecurity Landscape

White & Case Partners John Timmons and Clara Hainsdorf explore the key issues for organizations grappling with NIS 2 compliance in light of the complex implementation landscape. 

Read 1 min. article

Ransomware Payments: New legislative proposals in the UK

On 14 January 2025, the Home Office opened a public consultation (the "Consultation") on proposals seeking to address the growing threat and impact of ransomware in the UK.

Read 6 min. article
data centres

2024

NYDFS Releases Artificial Intelligence Cybersecurity Guidance For Covered Entities

On October 16, 2024, the New York State Department of Financial Services (the "DFS"), under its Cybersecurity Regulation—23 NYCRR Part 500—issued a memorandum providing guidance on the risks posed by artificial intelligence ("Guidance Memo").

Read 8 min. article

SEC Will Prioritize AI, Cybersecurity, and Crypto in its 2025 Examination Priorities

On October 21, 2024, the US Securities and Exchange Commission ("SEC") Division of Examinations ("Examination Division") announced its 2025 Examination Priorities ("Report"). Investment advisers and broker-dealers should ensure that policies, procedures and surveillance efforts related to these priorities address concerns outlined in the Report.

Read 3 min. article

SEC Enforcement Heats up on Key Public Company Topics: Cyber Disclosure, Director Independence and Regulation FD

The U.S. Securities and Exchange Commission's ("SEC") Division of Enforcement has recently brought a spate of enforcement actions relating to key topics for public companies. These include enforcement actions related to cybersecurity incident disclosure, director independence and Regulation Fair Disclosure ("Reg FD") violations, which are described below, and actions based on Section 13 and 16 beneficial ownership filings, as discussed in our prior alert.

Read 13 min. article

Judge Rejects SEC’s Aggressive Approach to Cybersecurity Enforcement

On July 18, 2024, a New York federal judge dismissed most of the US Securities and Exchange Commission's ("SEC") claims against SolarWinds Corp. ("SolarWinds" or the "Company") and its Chief Information Security Officer ("CISO"), Timothy G. Brown, in connection with the Company's cybersecurity practice.

Read 10 min. article

NIS 2 Directive: Navigating the challenges of implementation, impact, and scope

The NIS 2 directive establishes a regulatory framework aimed at improving the level of cybersecurity across the EU.

Read 1 min. article

SEC’s Corp Fin Director Issues Statement on Cybersecurity Incident Disclosures

On May 21, 2024, the SEC's Director of the Division of Corporation Finance issued a statement on cybersecurity incident disclosures in light of the SEC's new cybersecurity disclosure rules. Our summary of this statement and key take-aways from White & Case's survey of cybersecurity disclosures is below.

Read 6 min. article

2023

The SEC’s Charges Against SolarWinds and its Chief Information Security Officer Provide Important Cybersecurity Lessons for Public Companies

On October 30, 2023, the US Securities and Exchange Commission ("SEC") announced that it filed charges against SolarWinds Corp. ("SolarWinds" or the "Company") and its Chief Information Security Officer ("CISO") in connection with the SEC Division of Enforcement's ("Enforcement Division") investigation of a cyberattack.

Read 10 min. article

SEC Adopts Mandatory Cybersecurity Disclosure Rules

On July 26, 2023, the Securities and Exchange Commission ("SEC"), in a 3-2 vote, adopted rules that will require public companies to make prescribed cybersecurity disclosures.

Read 22 min. article

Shaping the future of digital and cybersecurity governance

In this brief three-minute video, London-based partner Lawson Caisley, Chair of White & Case's Global Cyber Risk Committee, shares his insights on governing cyber risk at the corporate level and some of the challenges of cyber risk management in the boardroom. Filmed at the Digital Directors Network (DDN) Domino 2023 conference on digital and cybersecurity governance.

Read 1 min. article
cybersecurity_square_800x800_4

Prioritizing cybersecurity at the corporate level

In this short three-minute video, Washington, DC–based partner F. Paul Pittman discusses the implications of the proposed new SEC rules on cybersecurity governance and what corporate boards can do now. Filmed at the Digital Directors Network (DDN) Domino 2023 conference on digital and cybersecurity governance.

Read 1 min. article
digital mesh

Cybersecurity Developments and Legal Issues

The potential for cybersecurity threats and attacks looms large and the technology companies developing new products and services play a constant game of cat-and-mouse with hackers and cybercriminals for control of cyberspace. Here are six points to consider when analyzing cybersecurity risks and protections.

Read 9 min. article
client alert image

Directors face personal liability over cybersecurity failures

In an article for The Times, White & Case partner Lawson Caisley discusses why it could become increasingly common for UK directors to "face personal liability and regulatory censure as a result of their company suffering or mishandling a cyberbreach".

Read 1 min. article
wafer circuit detail

2022

Director liability for cyber breaches: transatlantic warning signs?

Two legal cases in the US in the past month suggest that regulators and prosecutors are becoming more determined to take personal action against directors and senior executives who fail to deal adequately with cyber security breaches.  

Read 3 min. article
arrow

SEC Proposes Mandatory Cybersecurity Disclosure Rules

On March 9, 2022, the Securities and Exchange Commission ("SEC") proposed rules that would require public companies to make prescribed cybersecurity disclosures.

Read 14 min. article

2021

Legal 500's In-House Lawyer Magazine Autumn - Commercial Litigation Focus (Germany)

In The Legal 500's newly released In-House Lawyer Magazine a group of White & Case lawyers has contributed a legal briefing on trends in German commercial litigation.

Read 1 min. article
magazine pile

AAA plc & ors v Persons Unknown: Cyber Activism or Blackmail?

In recent years, demands for payments in cryptocurrencies have become the ransom of choice for cyber extortionists and other online frauds. As a result, the English Court's powers are increasingly being called upon.

Read 5 min. article
orange background

Contacts

SEC’s Corp Fin director issues statement on cybersecurity incident disclosures

Key Take-Aways from White & Case Survey of Cybersecurity Disclosures

Alert
|
6 min read

On May 21, 2024, the SEC's Director of the Division of Corporation Finance issued a statement on cybersecurity incident disclosures in light of the SEC's new cybersecurity disclosure rules. Our summary of this statement and key take-aways from White & Case's survey of cybersecurity disclosures is below.

The statement advises on (1) when disclosure should be made under an Item 1.05 Form 8-K (Material Cybersecurity Incidents), versus another Item, such as Item 8.01 (Other Events), and (2) materiality determinations generally for cybersecurity incidents. The statement by Erik Gerding was provided in his official capacity as the Commission's Director of Division of Corporation Finance but notes that it does not necessarily reflect the views of the Commission and does not alter or amend applicable law.1

Summary of Gerding’s Statement

In summary, Director Gerding advises the following in his statement: 

  • Item 1.05 for Material Cybersecurity Incident Versus Item 8.01 for Immaterial Incidents. In cases where a company chooses to voluntarily disclose a cybersecurity incident for which it has not yet made a materiality determination (or a cybersecurity incident that the company already determined was not material), the "Division of Corporation Finance encourages the company to disclose that cybersecurity incident under a different item of Form 8-K (for example, Item 8.01)" titled "Other Events" – rather than under the newly adopted Item.1.05 of the Form 8-K titled "Material Cybersecurity Incidents."
  • Item 8.01 Form 8-K for Immaterial Incident, Followed by Item 1.05 if Incident Becomes Material. If a company chooses to disclose an immaterial incident (or one for which it has not yet made a materiality determination) under Item 8.01 of Form 8-K, and it subsequently determines that the incident is material, it should file an Item 1.05 Form 8-K within four business days of such subsequent materiality determination. That subsequent Form 8-K on Item 1.05 may refer to the earlier Item 8.01 Form 8-K and will need to satisfy the requirements of Item 1.05.

In addition, Director Gerding addresses the following:

  • Assess All Relevant Factors to Determine Materiality. In determining whether a cybersecurity incident is material, companies should assess "all relevant factors" – in particular, a materiality assessment should "not be limited to the incident's impact on the company's financial condition and results of operation" and should "consider qualitative factors alongside quantitative factors," such as whether the incident will harm its "reputation, customer or vendor relationships, or competitiveness" as well as consider "the possibility of litigation or regulatory investigations or actions, including regulatory actions by state and Federal Governmental authorities and non-U.S. authorities."
  • Ability to Determine a Cybersecurity Incident is Material, Before Impacts are Known. In cases where a cybersecurity incident is so significant that a company concludes that it is material even though the company has not yet determined its impact (or reasonably likely impact), the company should disclose the incident in an Item 1.05 Form 8-K, include a statement noting that the company has not yet determined the impact (or reasonably likely impact) of the incident, and then amend the Form 8-K to disclose the impact once that information is available. As the statement notes, the initial Form 8-K filing should still "provide investors with information necessary to understand the material aspects of the nature, scope, and timing of the incident, notwithstanding the company's inability to determine the incident's impact (or reasonably likely impact) at that time."

The Director's statement explains that it is "not intended to discourage companies from voluntarily disclosing cybersecurity incidents for which they have not yet made a materiality determination, or from disclosing incidents that companies determine to be immaterial." Rather, the intent of the statement is to "encourage the filing of such voluntary disclosures in a manner that does not result in investor confusion" and it acknowledges the value of such voluntary disclosures to investors, the marketplace, and ultimately to companies. At the same time, the statement emphasizes that, as noted in the adopting release, "Item 1.05 is not a voluntary disclosure, and it is by definition material because it is not triggered until the company determines the materiality of an incident." As a result, the statement posits that "if all cybersecurity incidents are disclosed under Item 1.05, then there is a risk that investors will misperceive immaterial cybersecurity incidents as material, and vice versa."

White & Case Survey of Disclosures

White & Case's Public Company Advisory Group has been tracking Form 8-K cybersecurity incident disclosures since December 18, 2023, the effective date of the new rules. Between December 18, 2023, and May 23, 2024, 22 companies filed a total of 35 cybersecurity incident-related 8-Ks, either disclosing cybersecurity incidents or updating information on previously disclosed incidents:

  • 22 were Form 8-Ks and 13 were Form 8-K/As to update previous disclosures
  • 26 of these were under Item 1.05 "Material Cybersecurity Incidents"
  • 7 of these were under Item 8.01 "Other Events"
  • 2 of these were under Item 7.01 "Regulation FD Disclosure"2
  • Of the 26 filed under Item 1.05, a total of 23, or 88%, explicitly stated that they did not have a material impact or that the company had not yet made a materiality determination regarding the incident.
  • Of the nine filed under other items (Item 8.01 or Item 7.01), a total of eight, or 89%, explicitly stated that they did not have a material impact or that the company had not yet made a materiality determination.

For more information on our survey, including data on the actual impacts disclosed and timing of the disclosures, as well as survey information on annual report on Form 10-K/20-F cybersecurity disclosures, please contact the authors of this client alert. 

Conclusion

Director Gerding's statement was issued in an environment that provides numerous challenges for public companies as they consider how, when and whether to disclose information about a cybersecurity incident. Companies are routinely subject to cybersecurity incidents, the vast majority of which are not significant, and beyond an item number for a Form 8-K,3 companies are weighing how, when and whether to disclose these incidents in the face of potential media scrutiny, notification requirements under various cybersecurity incident and data breach notification regulations, the potential for regulatory scrutiny and enforcement,4 threats of private action from the plaintiff's bar, as well as volatile developments with respect to the cybersecurity incidents, among other concerns. Accordingly, as companies consider their disclosures on cybersecurity incidents, the focus should remain on the controls necessary to determine whether an incident is material and on the substantive disclosures that will ultimately be helpful for investors and companies in light of the applicable facts and circumstances.

The following White & Case attorneys authored this alert: Maia Gez, Scott Levi, F. Paul Pittman, Michelle Rutta, Joel Cohen, Tami Stark, Danielle Herrick

1 See Footnote 1 of the statement, which also notes that "this statement, like all staff statements, has no legal force or effect: it does not alter or amend applicable law, and it creates no new or additional obligations for any person."
2 Note that three of the Form 8-Ks filed under Item 1.05 also filed Item 7.01 disclosure in the same Form 8-K.
3 The item numbers in a Form 8-K tend to be a technical aspect of disclosure and SEC form compliance. With regard to fundamental antifraud liability concerns, it is important to remember that the substance of the disclosure is the information being provided to investors, regardless of the item number used. For additional considerations, also see Instruction 3 of the Form 8-K and market practice for using the Item 5.03 item number even when not technically required. 
4 See our client alert on the Solarwinds case. The defendants in the case have since filed a motion to dismiss the case and rejected the SEC's claims, arguing that its disclosure in a Form 8-K had disclosed the key facts about the attack only one trading day after the company learned of the incident. 

White & Case means the international legal practice comprising White & Case LLP, a New York State registered limited liability partnership, White & Case LLP, a limited liability partnership incorporated under English law and all other affiliated partnerships, companies and entities.

This article is prepared for the general information of interested persons. It is not, and does not attempt to be, comprehensive in nature. Due to the general nature of its content, it should not be regarded as legal advice.

© 2024 White & Case LLP

Top